IMAFE Incognito↗
Private files. Local processing. Clear boundaries.
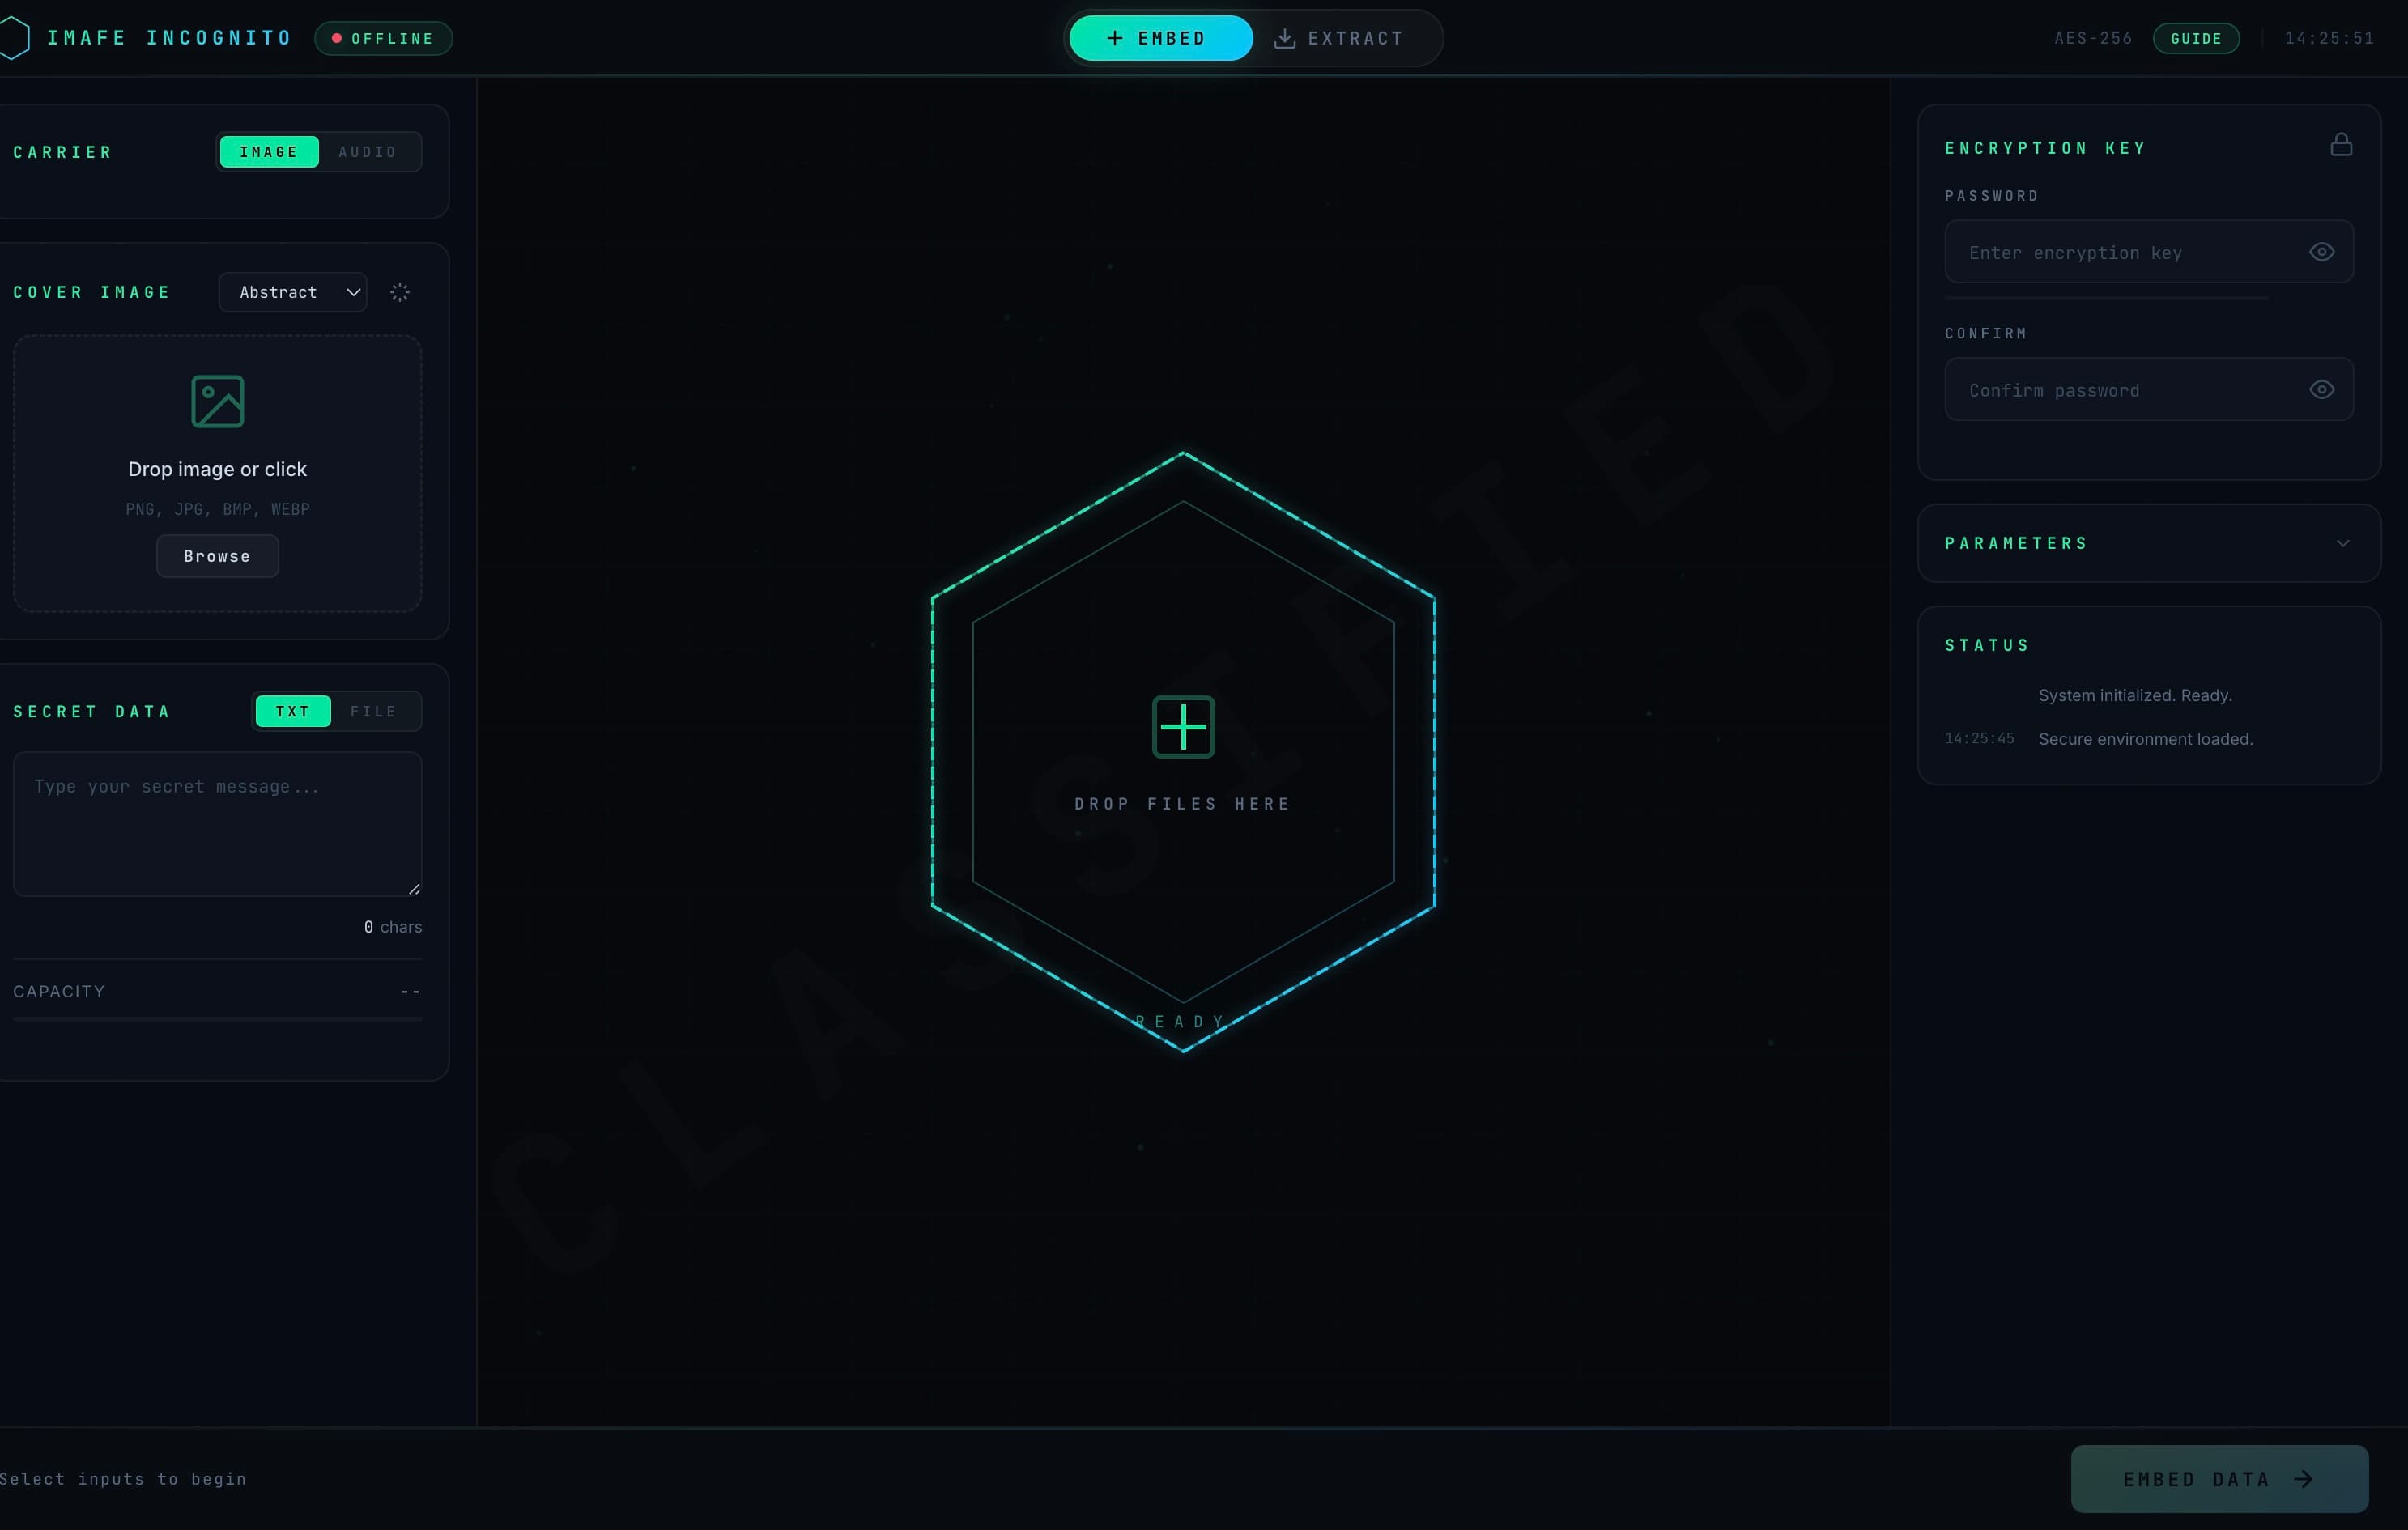 ACTUAL APPLICATION CAPTURE
Open it.
Inspect the work.
A real development capture of the Electron interface, backed by public Python source and rerun encryption and steganography tests.
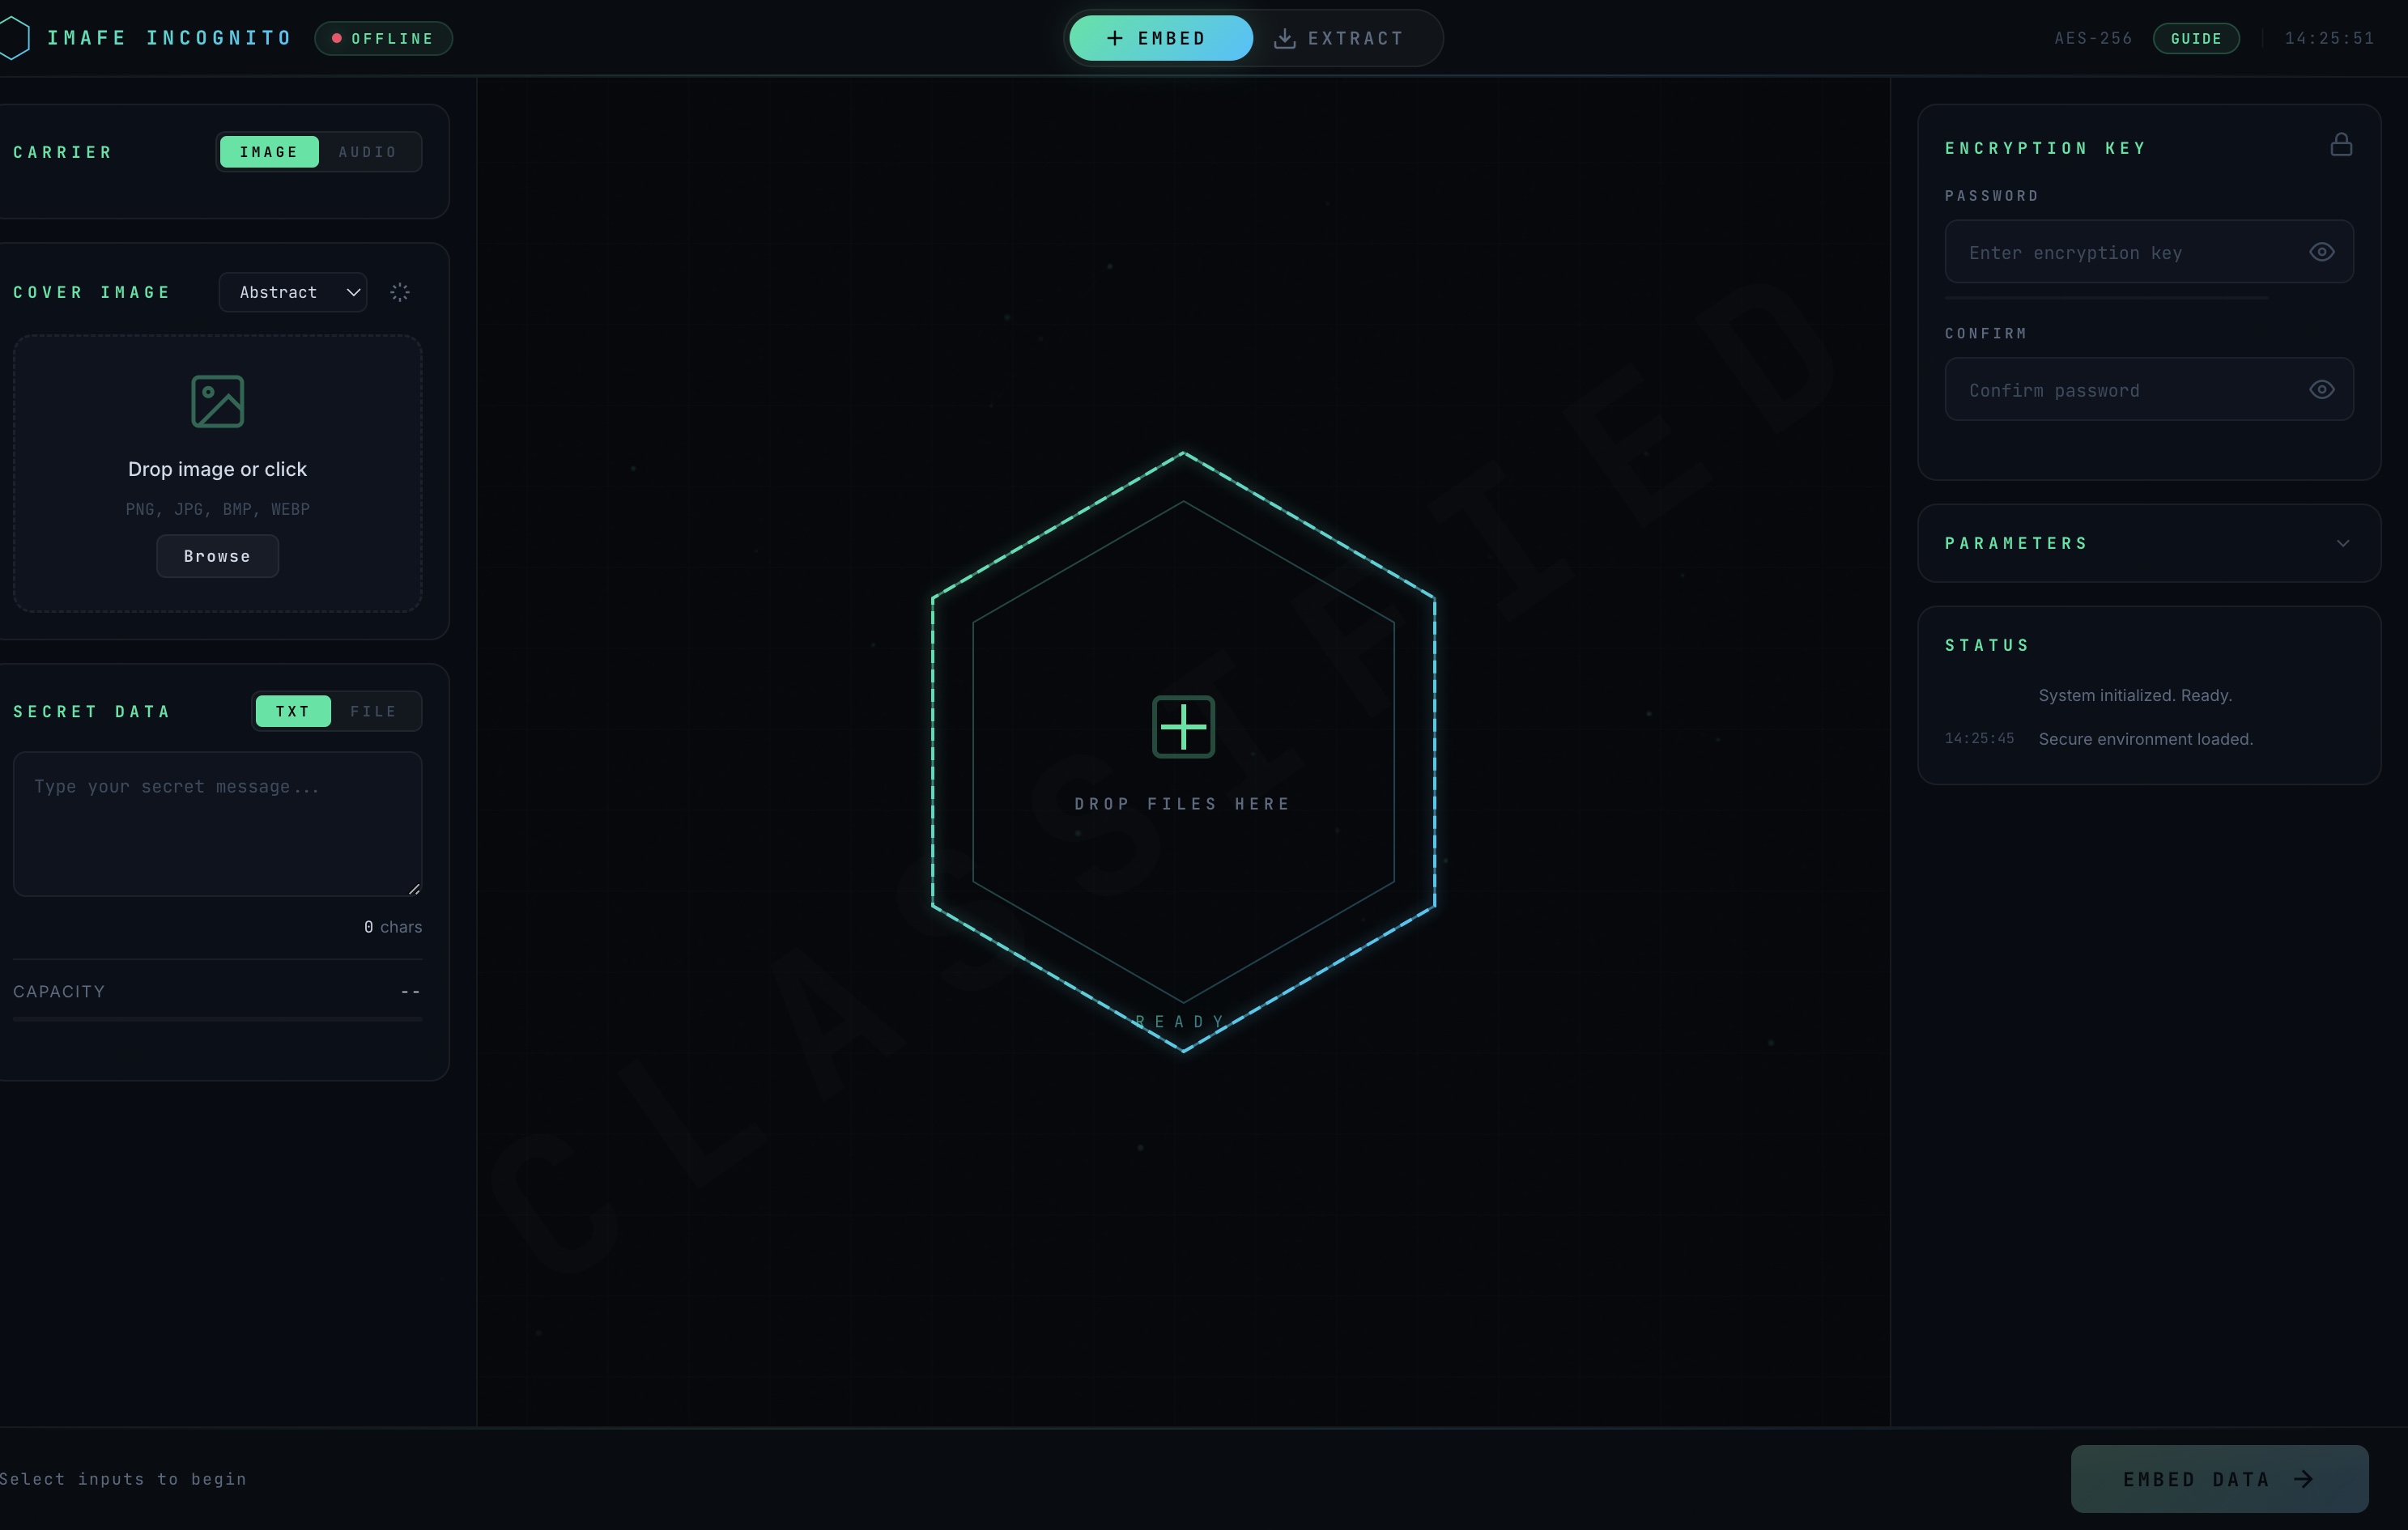 Open full size ↗
def test_file_encryption_round_trip(tmp_path: Path) -> None:
    source = tmp_path / "source.bin"
    encrypted = tmp_path / "source.imfe"
    restored = tmp_path / "restored.bin"
    payload = b"IMAFE round-trip test\x00\xff" * 32
    source.write_bytes(payload)

    encrypt_file(source, encrypted, "correct horse battery staple")
    assert is_encrypted_file(encrypted)

    decrypt_file(encrypted, restored, "correct horse battery staple")
    assert restored.read_bytes() == payload
Actual test code writes a binary payload, encrypts it, decrypts it, and compares the restored bytes. The password shown is a public test fixture.
10 tests passed on September 14, 2026, covering encryption, password rejection, image/audio steganography, and file-type detection. Educational software, not independently audited.
A real problem.
A considered solution.
A desktop privacy workflow needs a clear boundary between the interface, local file processing, and encryption logic.
What I worked on.
The application combines encrypted file storage with image and audio steganography. An Electron interface communicates with a local Python service; files stay on the user’s computer.
Select file
The desktop app accepts a local file. There is no remote file-processing service.
A guided explanation of the project architecture. This explorer does not connect to production systems.
Use authenticated encryption.
AES-256-GCM and PBKDF2-HMAC-SHA256 with per-message salts support password-based encrypted containers.
Constrain the desktop boundary.
The sandboxed renderer uses a narrow preload bridge. The local API receives a fresh session token when the application starts.
Test round trips and failures.
The public suite covers encryption, wrong-password rejection, image/audio carriers, capacity handling, and format detection.
A public implementation connecting desktop UI, local services, cryptographic primitives, and automated round-trip tests.
Educational project; not independently audited security software. Its steganography is not claimed to be undetectable.
Campus Sports
Arlington, TX · Open to Seattle and US relocation